Package Name:com.foor.secnotes.handbook
SHA-256:5f8fdf6d5a9b9639d3e60d550afa3da4548411ab0975a459ec17e6862fef3e5a
Show More
SecNotes is the ultimate offline pocket handbook for penetration testers, security researchers, CTF competitors, and cybersecurity students.
Designed for quick field reference, air-gapped lab environments, and exam preparation (OSCP, PNPT, CEH, Security+), SecNotes delivers concise, actionable checklists and interactive utilities directly to your device—100% offline with zero latency.
════════════════════════════════════════
CORE KNOWLEDGE MODULES (37+ GUIDES)
════════════════════════════════════════
• AI & LLM Security: Transformer mechanics, tokenization, LoRA & QLoRA fine-tuning, prompt injection, RAG vector poisoning, model deserialization RCE (Pickle/SafeTensors), and Model Context Protocol (MCP) tool security.
• Web Application Security: SQL injection (SQLi), SSRF & cloud metadata pivots (AWS IMDSv1/v2), JWT attacks, LFI/RFI log poisoning, Server-Side Template Injection (SSTI), GraphQL introspection, and HTTP request smuggling.
• Linux Privilege Escalation: SUID abuse, GTFOBins binaries, sudoers misconfigurations, LD_PRELOAD hooks, kernel vulnerabilities, and capability abuse.
• Windows Privilege Escalation: Token impersonation (Potato family), unquoted service paths, always install elevated, and SAM/LSA registry secrets dumping.
• Active Directory Auditing: Kerberoasting, AS-REP roasting, BloodHound domain mapping, Golden/Silver tickets, and pass-the-hash methodologies.
• Network & Ports: Fast port enumeration profiles for SMB (139/445), FTP (21), SSH (22), SNMP, RPC, and Nmap scan cheat sheets.
• Reconnaissance & OSINT: Subdomain discovery, virtual host fuzzing, Amass, Subfinder, and DNS zone transfer queries.
• Cryptography & Hashes: Hashcat modes, John the Ripper formats, hash identifier reference, and password-cracking workflows.
• Mobile Application Pentesting: Android APK decompilation, Jadx, Frida SSL pinning bypass, and root detection evasion.
════════════════════════════════════════
BUILT-IN INTERACTIVE TOOLS
════════════════════════════════════════
• Reverse Shell Generator: Instant multi-language payload generator (Bash, Python, Netcat, PowerShell, PHP, Socat, Perl, Ruby) with real-time IP and port injection.
• Data Encoder / Decoder: UTF-8 safe Base64, URL component, Hex (raw, spaced, \x escape formats), and HTML entity transformation.
• JWT Inspector: Instant client-side JSON Web Token parser with header and payload JSON formatting, claim breakdown (sub, iss, iat), expiration status calculation, and insecure algorithm flagging (alg: "none").
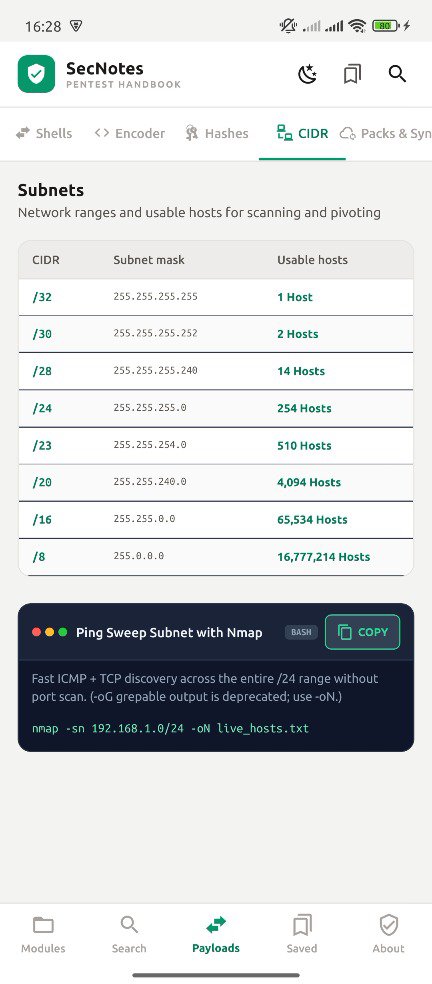
• CIDR Subnet Calculator: Quick reference for IPv4 network masks, usable host counts, and subnet bounds.
════════════════════════════════════════
MOBILE-FIRST DESIGN
════════════════════════════════════════
• 100% Offline Access: All guides, code snippets, and calculators are bundled into flash storage. Access reference guides in planes, basements, or air-gapped networks.
• Instant Sub-Millisecond Search: Find any port, command flag, payload, or CVE technique across the entire handbook in real time.
• One-Tap Copy with Haptics: Tap any command snippet to copy directly to your clipboard with tactile feedback.
• Dual Aesthetic Themes: Switch between True OLED Pure Black mode (energy-saving on AMOLED displays) and Clean Paper Light mode with a single header tap.
════════════════════════════════════════
ETHICAL USE & DISCLAIMER
════════════════════════════════════════
SecNotes is designed strictly for educational, defensive, and authorized security auditing purposes. The commands, techniques, and payloads contained within are intended to assist cybersecurity professionals, authorized penetration testers, systems administrators, and students participating in controlled environments (CTFs, HackTheBox, TryHackMe).
Unauthorized access to computer systems, networks, or devices without explicit prior authorization is illegal. The creators assume no liability for misuse.
Latest Version
1.0.0Uploaded by
Nur Fauzan
Requires Android
Android 7.0+
Category
Free Tools AppContent Rating
Everyone
Security Report
Check Now
Report
Flag as inappropriateLast updated on Oct 22, 2026
This release includes minor bug fixes and general improvements. Update to the latest version for the best experience.





APKPure - A multi-platform app store primarily focused on Android, providing extensive app-related content. Discover the app you want easier, faster, and safer, with quick and efficient downloads and installations.